
Third Party Cyber Risk Management: How to Protect Your Business from Supply Chain Breaches
Third party cyber risk management is the practice of identifying and reducing the cybersecurity threats introduced by outside vendors, contractors, and software providers who have access to your company data. Establishing a strong supply chain defense is essential for preventing data breaches and ensuring operational continuity.
According to a recent report by SecurityScorecard, 35.5% of data breaches were linked to third-party access. Two exploited file transfer software vulnerabilities accounted for 63.5% of all third-party vulnerability-driven breaches.
The Rising Threat of Supply Chain Attacks
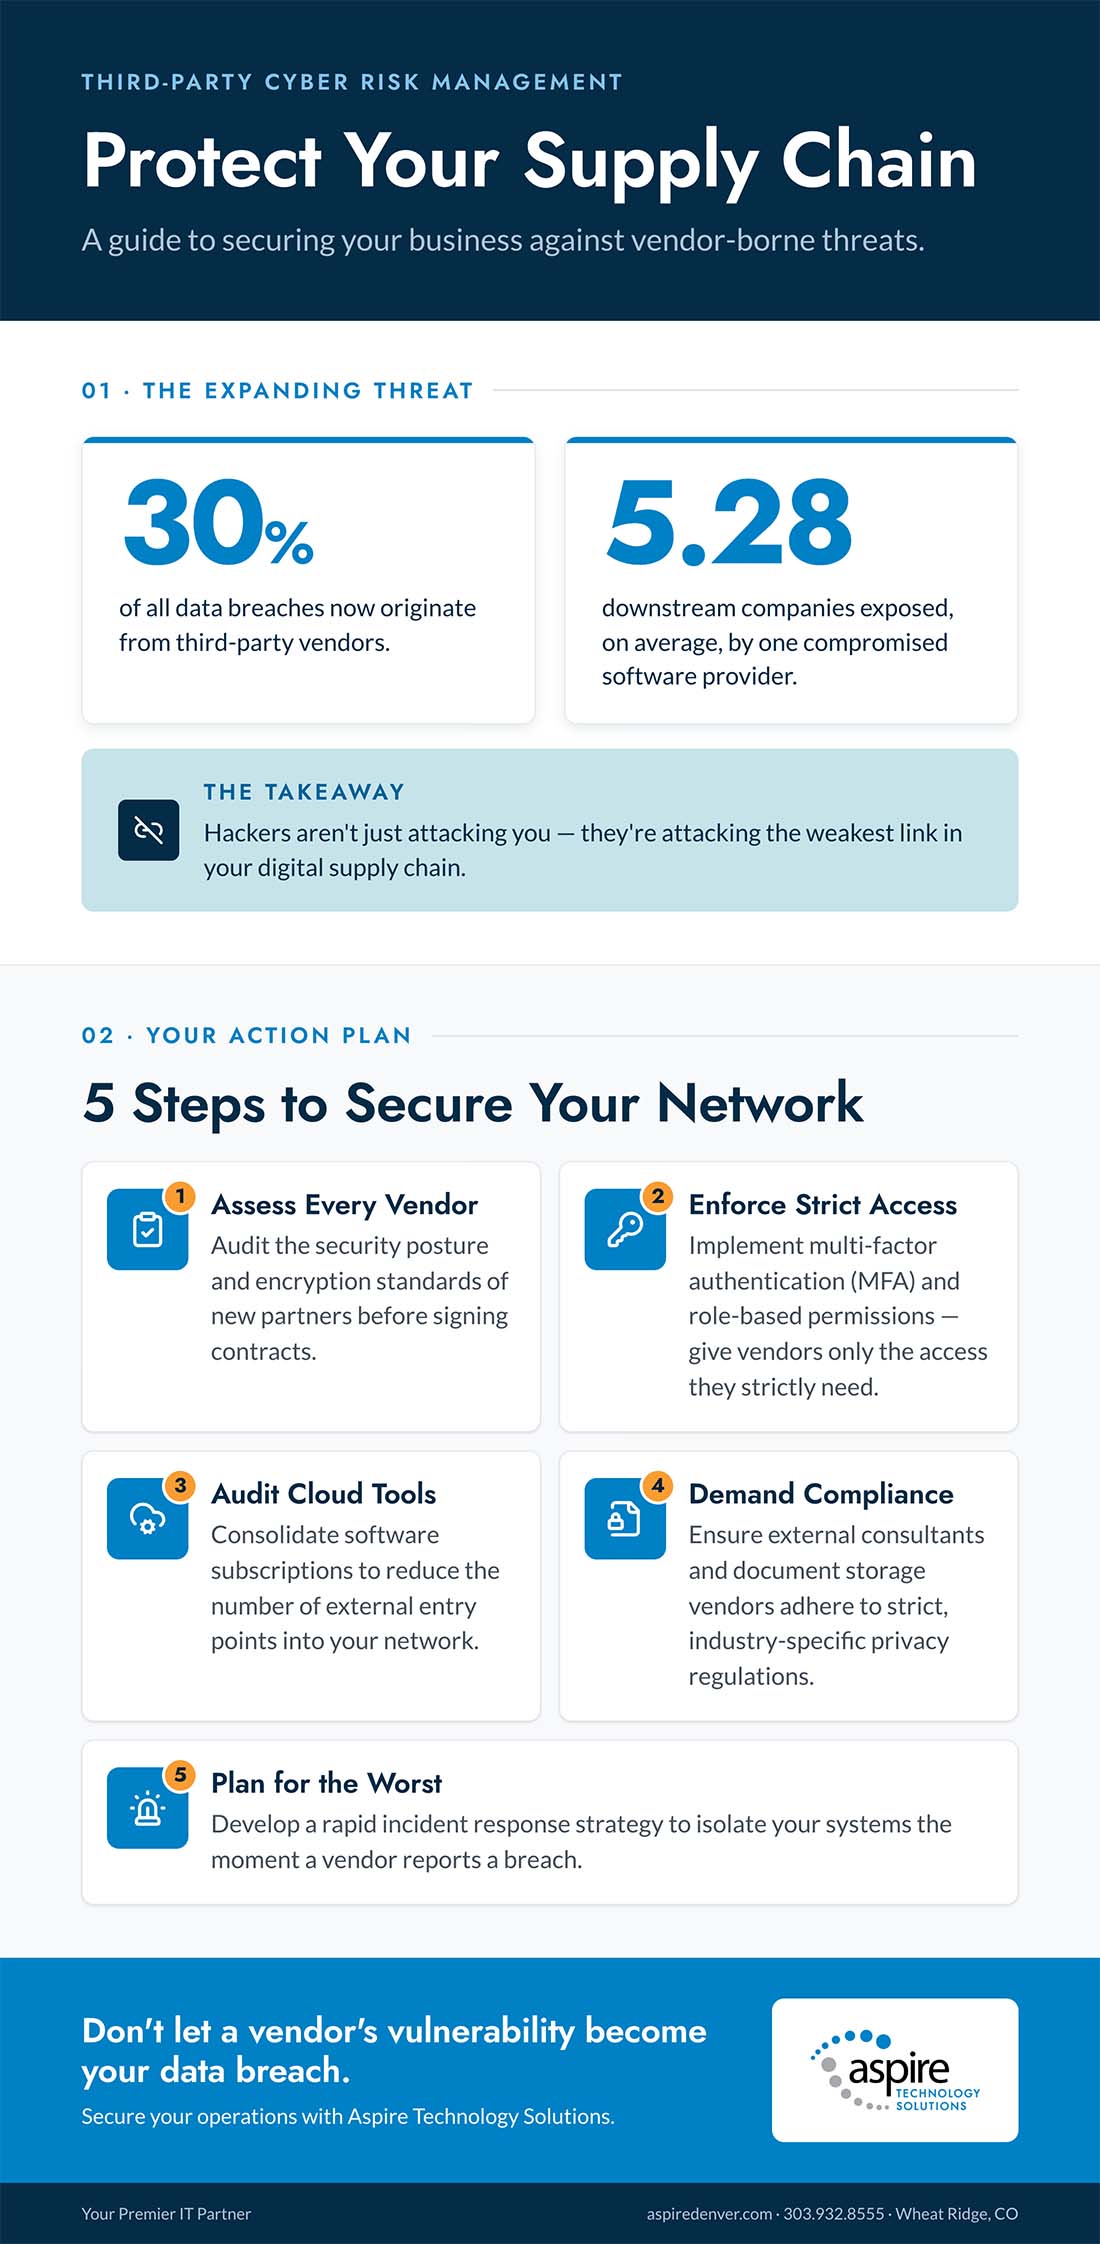
Over the last year, the digital supply chain has become the primary target for cybercriminals. Hackers realize that instead of attacking a dozen individual small businesses, they can breach a single managed service provider, accounting software vendor, or cloud storage platform to access all their downstream clients simultaneously. Recent cybersecurity data highlights this growing risk, as research shows that for every single vendor breached, an average of 5.28 downstream companies are publicly compromised. Because this cascading effect is so lucrative for attackers, third-party compromises now account for 30% of all data breaches.
What is Third Party Cyber Risk Management?
Organizations rely on external vendors for payroll processing, software applications, and IT support. Third party cyber risk management is the framework used to ensure these partners maintain strict security standards. Hackers frequently target the weakest link in a corporate supply chain to bypass primary internal security controls. If your accounting software provider suffers a data breach, your sensitive financial information becomes compromised. Effectively managing this risk involves continuous monitoring, strict access controls, and detailed vendor assessments.
5 Strategies for Effective Third Party Cyber Risk Management
Implementing a robust defense against supply chain attacks requires proactive planning. Use these five strategies to secure your operations.
1. Conduct Regular Vendor Risk Assessments
Before signing a contract with a new vendor, evaluate their security posture. Request documentation on their encryption standards and incident response plans. Treating vendor security as a core business requirement helps you partner safely with outside organizations.
2. Implement Strict Access Controls
Vendors should only have access to the specific data and systems required to perform their jobs. Enforce multi-factor authentication and role-based permissions across your network. Limiting access prevents a compromised vendor account from navigating freely through your sensitive files.
3. Monitor Cloud Subscriptions
Software applications frequently introduce vulnerabilities. Managing your external software environment is closely tied to cloud computing cost management. Auditing and consolidating your cloud tools reduces the number of external entry points hackers can exploit.
4. Ensure Industry Compliance
Certain industries face strict regulatory requirements regarding data protection. Maintaining proper IT compliance for law firms requires ensuring that every external legal consultant and document storage vendor adheres to mandated privacy laws. Make sure your contracts include formal compliance clauses.
5. Develop an Incident Response Plan
Create a documented incident response plan that outlines exactly how your team will react if a vendor is compromised. Fast communication and rapid system isolation minimize the overall impact of a cyberattack.
The Hidden Costs of a Vendor Data Breach
The financial impact of a supply chain breach includes immediate remediation efforts and significant regulatory fines for failing to protect consumer data. A breach damages client trust and brand reputation. Proactive cybersecurity for professional services provides a strong return on investment by preventing costly data leaks and operational downtime.
Secure Your Supply Chain with Aspire Technology Solutions
Managing vendor security requires dedicated time and specialized expertise. Partnering with an experienced managed IT provider takes the guesswork out of protecting your business. At Aspire Technology Solutions, our team helps Denver businesses assess external risks, monitor network activity, and enforce strict security policies. Contact us today to learn how we can strengthen your supply chain defenses.